Create a Strong Memorable Password: A Practical Guide
Key takeaways
- Build memorable passphrases from randomly selected, unrelated words rather than quotes, personal details, or predictable substitutions.
- Use a different password for every account so one exposed credential cannot open several services.
- Let a password manager generate and store most passwords, and reserve memorization for credentials you must enter yourself.
- Enable multifactor authentication and prepare recovery methods before you need them.
- Replace exposed passwords wherever they were reused, then review account activity and recovery settings.
To create a strong memorable password, use a long passphrase made from randomly selected, unrelated words, and never reuse it on another account. For most other logins, let a password manager generate and store a unique password so you do not have to memorize it.
The goal is not to invent something that looks complicated. It is to choose something an attacker cannot readily predict while keeping your own login routine manageable.
That means treating strength, uniqueness, and account recovery as separate jobs. A memorable passphrase helps with the first; a password manager and multifactor authentication help with the others.
Why password strength and uniqueness both matter
A password can fail in different ways. An attacker might guess a predictable choice, try credentials exposed by another service, or trick you into entering the password on a fraudulent login page.
Strength makes a password harder to guess. Uniqueness limits the damage when one service exposes your credentials. Neither replaces the other: a long password reused everywhere still creates a shared point of failure.
Length helps, but the way you select a password matters too. A familiar quotation can be long and still predictable. Adding an exclamation mark to a sports team name does not make the underlying choice random.
Our guide to password spraying versus brute-force attacks explains why attackers do not always need to exhaust every possible combination. Sometimes they simply try likely choices across many accounts.
For a broader foundation, CISA’s Secure Our World guidance covers strong passwords, password managers, and additional account protections.
How to create a strong memorable password step by step
A passphrase is a password made from multiple words. Its advantage is practical: unrelated words can be easier to remember than a similarly long string of arbitrary characters. But a sentence you invent is not automatically an unpredictable passphrase.
1. Decide whether you actually need to remember it
For an ordinary website account, use your password manager’s generator and save the result. There is little benefit in making every password memorable when software can handle that work.
Reserve your memorization effort for credentials you must enter without the manager, such as the password that opens your password vault.
2. Generate unrelated words randomly
Use a reputable password manager’s passphrase generator, or a dice-based method with a published word list and clear instructions. Follow the method rather than choosing words that feel random to you.
As a practical starting point, use five or six randomly selected words when the service permits the resulting length. That is a usability recommendation, not a universal guarantee: word-list size, selection method, and account protections also matter.
Do not select words from your biography, favorite books, or surroundings. Human choices tend to introduce patterns that a genuinely random selection avoids.
3. Make a memory aid after generating the words
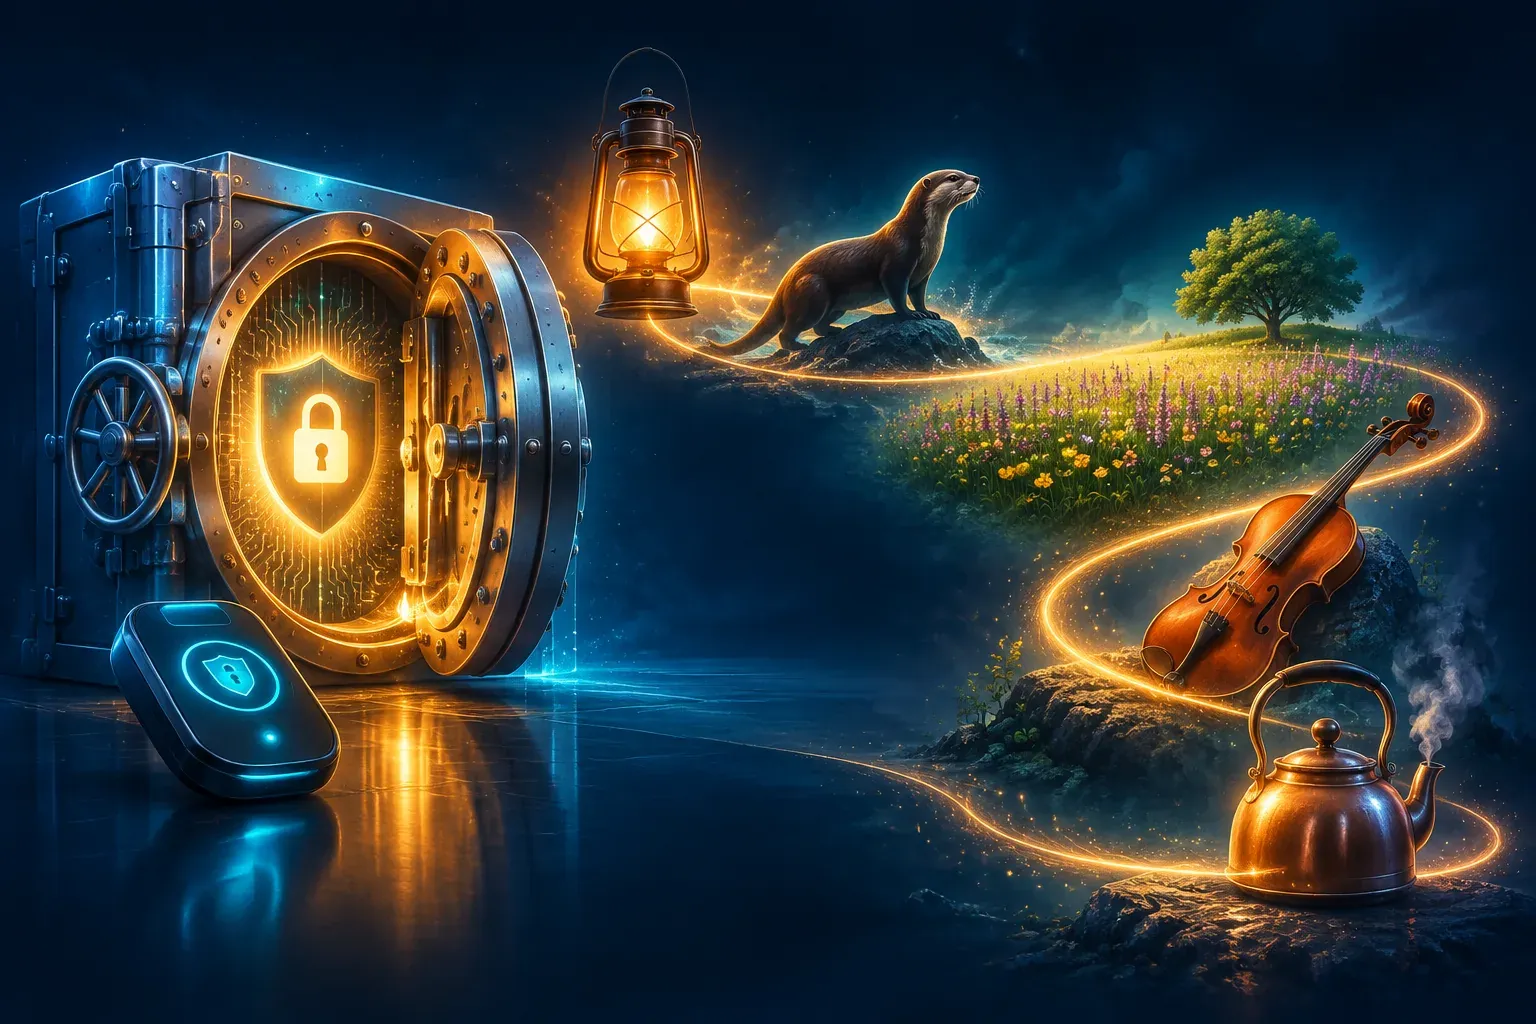
Imagine the generator produces an odd sequence involving a lantern, an otter, a meadow, a violin, and a kettle. Picture the otter carrying a lantern through the meadow while a violin plays from inside the kettle.
The story helps you remember the generated sequence. It should not determine the words in the first place. Do not use this published example as your password.
4. Adapt to the service without rebuilding the phrase
If the site accepts spaces or separators, choose a format you can type consistently. If it requires a number or symbol, satisfy that requirement without shortening the phrase or replacing the randomly selected words.
Separators improve readability; they do not compensate for predictable word choices. If a service rejects long passphrases, generate a unique password that fits its limits and store it in your manager.
5. Practice and prepare recovery
Practice entering the passphrase until you can recall it reliably. Avoid typing it into unfamiliar password-strength websites or sending it to yourself by email.
Set up a secure recovery method before relying on memory alone. Keep any emergency record somewhere physically protected, not beside the device it unlocks.
Which password patterns should you avoid?
The most useful test is not “Does this look complicated?” It is “Could someone predict how I made this?” Personal facts, familiar phrases, and repeated templates often fail that test.
| Approach | Main weakness | Better alternative |
|---|---|---|
| Pet name plus birth year | Uses discoverable or guessable details | Randomly generated words |
| Famous quote or lyric | Follows recognizable language | Unrelated, randomly selected words |
| Familiar word with letter substitutions | Preserves a predictable base word | A generated password or passphrase |
| One base password with a site suffix | Creates a reusable pattern | Independent passwords for each account |
| Short keyboard sequence | Follows a recognizable pattern | A longer, randomly generated choice |
Changing a to @ or adding a trailing number can satisfy a website’s rules without addressing predictability. Likewise, moving from one season name to the next is not a meaningful response to a compromised password.
Avoid password “systems” based on website names. If one credential becomes visible, the pattern may help someone infer your choices elsewhere.
Also distinguish online guessing from offline cracking. If attackers obtain password hashes—stored representations of passwords—they may be able to test guesses outside the service’s login controls. Our explanation of how hackers crack password hashes covers why password choice and the service’s storage protections both matter.
Use a password manager for everyday accounts
A password manager stores credentials in a protected vault and can generate different passwords for different services. It removes the pressure to choose something memorable every time you register.
Choose one that supports your devices, offers a password generator, explains its security approach, and provides recovery information you understand. Review its export options too, so moving to another manager remains practical.
For example, Bitwarden’s official website is one place to explore how a password manager works. Evaluate any product against your own device, sharing, and recovery needs rather than treating one brand as a universal answer.
A useful setup checklist is:
- Protect the vault with a unique, randomly generated passphrase.
- Enable multifactor authentication where available.
- Learn what happens if you forget the vault password.
- Secure recovery codes separately from the account they restore.
- Replace reused passwords, starting with email and sensitive accounts.
- Protect the devices that can access the vault.
Autofill can reduce copying and typing, but do not treat it as permission to ignore the website address. If credentials do not appear where expected, check the domain rather than immediately pasting the password.
A manager concentrates valuable information, so its protection deserves special attention. The benefit is that maintaining independent passwords becomes realistic rather than a memory exercise.
Add multifactor authentication and recovery safeguards
Even an excellent password can be stolen through phishing, malicious software, or a compromised service. Multifactor authentication, or MFA, adds another requirement beyond the password.
Where available, consider a passkey or security key, which can provide phishing-resistant authentication. Authenticator apps are another option; text-message codes can add protection, though they have limitations. Availability and recovery choices vary by service.
Prioritize your primary email account because it often receives password-reset messages for other accounts. Then protect financial services, your password manager, and accounts containing sensitive personal or work information.
Recovery deserves the same care as everyday login. Save backup codes securely, remove outdated recovery details, and avoid storing your only recovery method inside the account it is meant to restore.
NIST’s digital identity guidance provides the standards perspective on authentication. For service-side controls, the OWASP Authentication Cheat Sheet explains protections that complement an individual’s password choices.
What to do if a password may have been exposed
If you entered a password on a suspicious page, received a credible compromise notice, or found unfamiliar account activity, act through the service’s official website or app. Avoid following a password-reset link from an unexpected message.
- Change the affected password to a newly generated, unique one. Do not make a small variation of the old credential.
- Replace it anywhere else it was reused. Prioritize email and accounts that control money or sensitive information.
- Review active sessions and sign out unfamiliar devices. Use an option to sign out other sessions if available.
- Check recovery details and connected apps. Remove changes or access you do not recognize.
- Enable or review MFA. Replace exposed recovery codes when necessary.
- Investigate the cause. If you suspect malicious software or an unsafe device, address that before entering replacement credentials there.
A password change alone may not remove every form of access. Unfamiliar forwarding rules, recovery addresses, or connected applications can require separate attention. Contact the service’s support team if you cannot regain control.
The Bottom Line
To create a strong memorable password, generate unrelated words randomly, use the result for only one account, and build a memory aid around it. Let a password manager handle the passwords you do not need to memorize.
Start with your primary email account: replace any reused password, enable MFA, and verify recovery access. Then work through your remaining accounts, replacing shared credentials with independent ones.
Frequently Asked Questions
What makes a password strong and memorable?
A long passphrase made from randomly selected, unrelated words can combine unpredictability with easier recall. Build a mental image around the generated words, and use the passphrase for only one account.
How many words should a memorable passphrase contain?
Five or six randomly selected words can be a practical starting point when the service accepts the length. Security also depends on the word list and selection method, so a familiar sentence with the same number of words is not equivalent.
Are passphrases stronger than passwords with symbols?
Not automatically: length and unpredictability matter more than whether a credential looks complicated. A randomly generated password can be strong, while a predictable phrase with punctuation can still be weak.
Should I use a password manager or remember my passwords?
Use a password manager to generate and store unique credentials for most accounts. Focus on remembering the credentials you must enter without it, and prepare secure recovery methods.
Can I reuse a strong password on different websites?
No. If one service exposes the password, attackers may try it on other services, so each account should have an independent password.
Does multifactor authentication replace a strong password?
For accounts that still use passwords, MFA adds protection rather than making weak or reused passwords safe. Use a unique password, enable the strongest suitable authentication option available, and secure your recovery methods.
Read more on InnoVirtuoso
Enjoyed this? Subscribe to the InnoVirtuoso newsletter for practical AI, security and tech insights — and share your thoughts in the comments.