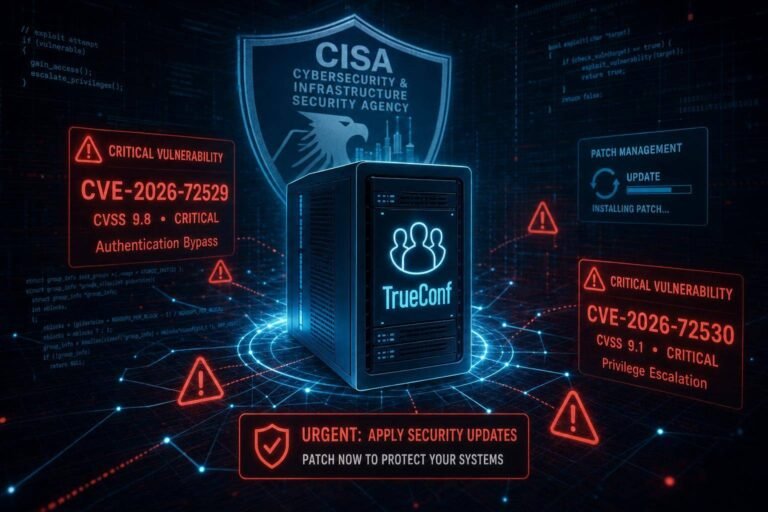
CISA Warns of Active Exploitation: Patch TrueConf Server CVE-2026-72529 and CVE-2026-72530 Now
Cyberattackers are actively exploiting two critical vulnerabilities in TrueConf Server—CVE-2026-72529 and CVE-2026-72530—and the U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent call for federal agencies to patch. This is not a theoretical risk. It’s a confirmed “exploited in the wild” situation targeting widely deployed video conferencing infrastructure. If your organization runs TrueConf…